Team
Every engagement is led by Brian Allen and delivered by senior practitioners assembled for it. We name the team in every proposal.
How we staff an engagement
We are deliberately small. That is a choice about who sits in the room with your board, not a limit on what we can take on.
Led by a principal
Brian Allen leads every engagement and is in every working session. There is no handoff to a delivery team you have not met.
Built to fit
We assemble two to four practitioners for each engagement from a group who have run risk, security, audit, and supervisory functions inside regulated institutions.
Named in the proposal
Every proposal names the people who will do the work, what each has done, and what each will do for you.
No bench
Nobody on an engagement is learning the job on your time. If a question needs a specialist we do not have, we say so and we find one.
Who you work with
Our practitioners have served as:
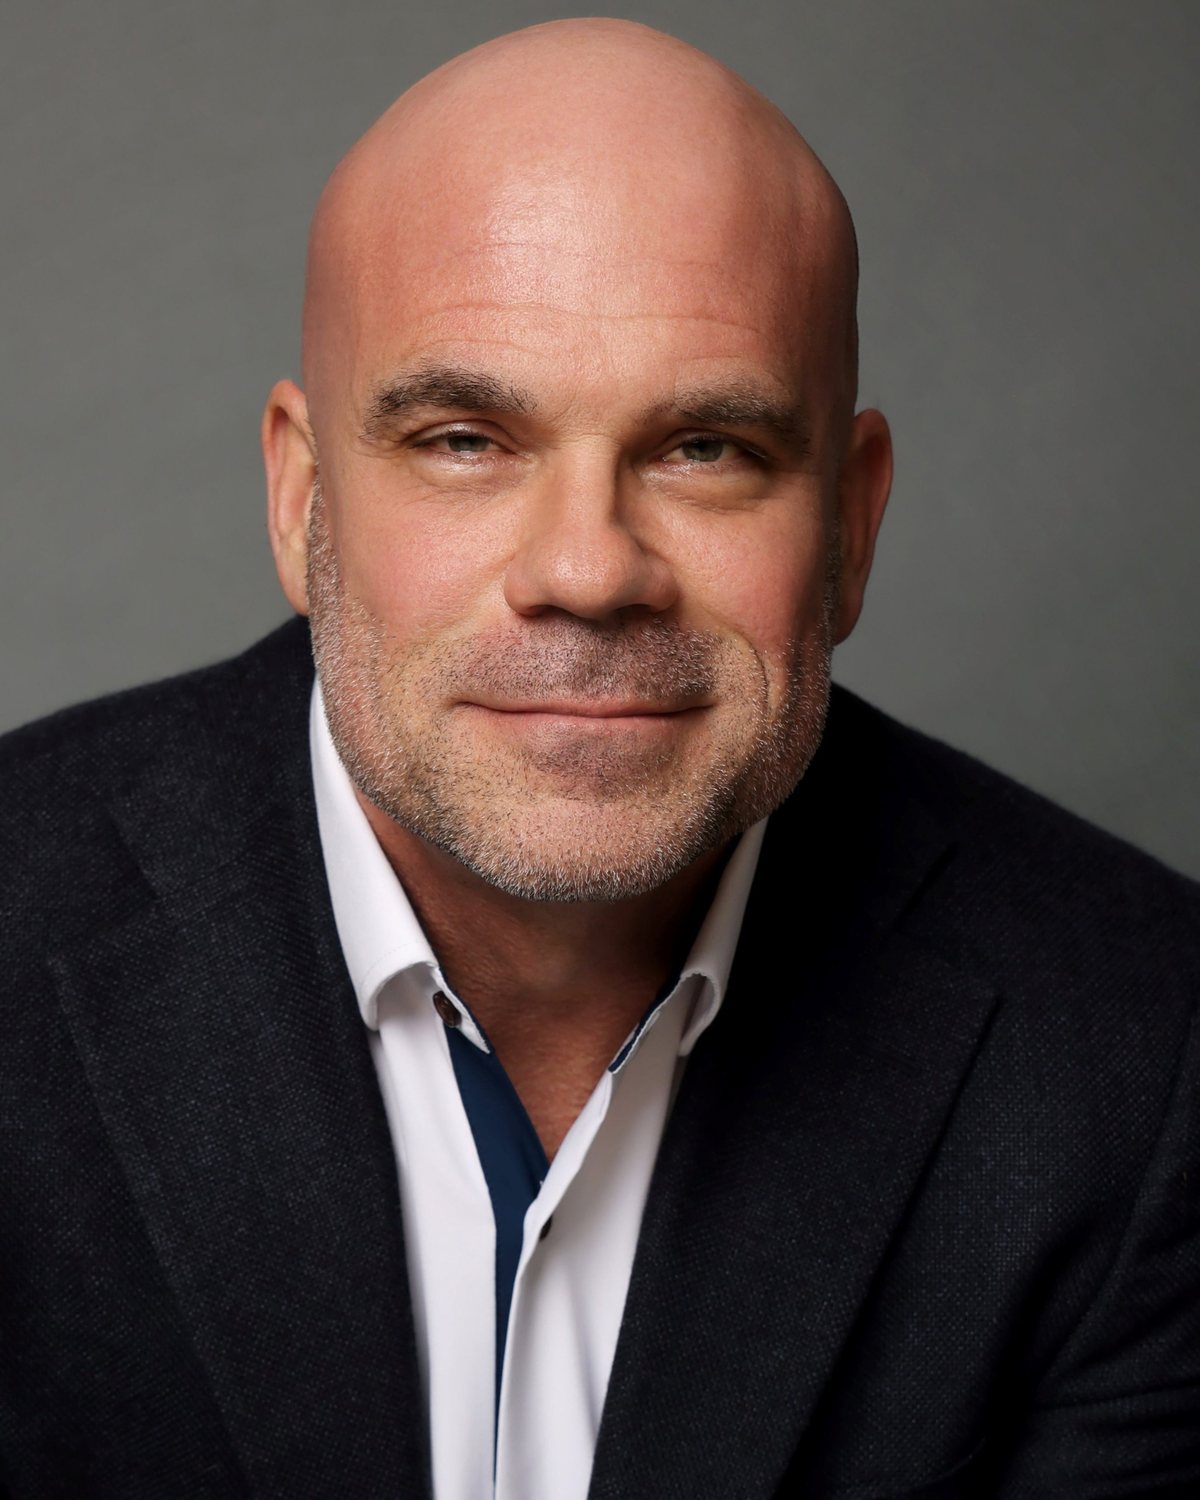
Brian J. Allen, Esq.
Brian Allen has spent his career on the side of the table where risk decisions get made. He served as Chief Security Officer and led Enterprise Risk Management at Time Warner Cable, a Fortune 100 company, and later as Senior Vice President of Emerging Technology Risk Management at the Bank Policy Institute, where he worked with the largest U.S. banks on the governance of AI and other emerging technologies. He founded the Center for AI Oversight, an independent nonprofit research and education organization that defines oversight governance for AI in regulated industries.
He is the author of Building a Cyber Risk Management Program (O'Reilly Media, 2023), co-author with Rachelle Loyear of Enterprise Security Risk Management: Concepts and Applications (Rothstein Publishing, 2017), and lead author of the forthcoming The AI Risk Compendium. He has delivered keynote addresses and speaks globally on risk governance.
If your board is asking what it should be asking about AI, start here.
A first conversation is 30 minutes with a senior member of our team. We listen to where you are and tell you plainly what we would look at first.